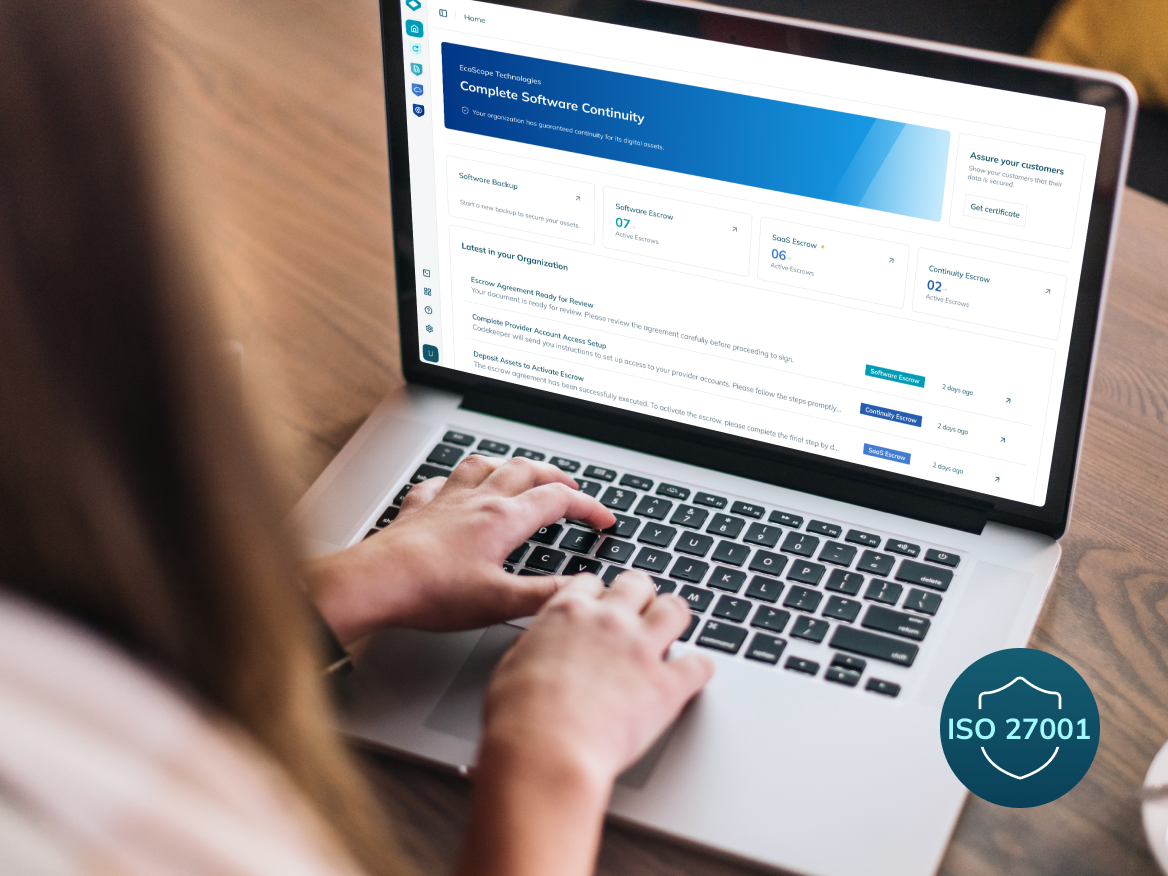
Build ISO 27001-ready supply chain resilience with software escrow
When your critical software vendors fail, your ISO 27001 controls crumble. Your organization faces immediate compliance gaps, system vulnerabilities, and lost certifications that destroy business credibility.
ISO 27001: What you need to know
What is ISO 27001?
Who needs to comply with ISO 27001?
Key ISO 27001 requirements
The software escrow — ISO 27001 connection
Let us help you with ISO 27001 readiness
Codekeeper's complete solutions for ISO 27001 requirements
Protection scope: On-premises software and applications
Protection scope: Cloud-based applications and services
Protection scope: Supporting infrastructure and services
Protection scope: All escrowed materials
Get ISO 27001 ready in 4 simple steps
Schedule your ISO 27001 assessment call
We'll review your software portfolio and flag which applications need escrow to meet ISO 27001 supplier requirements.
Select your preferred escrow protection strategy
Choose standard escrow protection or add verification testing for comprehensive recovery evidence.
Complete implementation with support
We'll coordinate vendor arrangements, draft legal frameworks, and establish automated processes for you.
Receive your compliance documentation
Get verified proof of your risk controls, including Software Resilience Certificates for audit evidence.
Codekeeper takes the complexity out of compliance
ISO 27001:2022 transition timeline
-
October 2022
ISO 27001:2022 officially published with updated Annex A controlsOrganizations begin transition planning from 2013 version -
April - May, 2024
Final deadline for new certifications under ISO 27001:2013All certification bodies must use 2022 version for new audits -
October 31, 2025
Transition deadline for existing ISO 27001:2013 certificatesOrganizations must complete recertification to 2022 version or lose certification -
Ongoing from 2025
Continuous surveillance audits under new control frameworkRegular management reviews and risk assessments required for maintained certification
October 2022
April - May, 2024
October 31, 2025
Ongoing from 2025
The cost of inadequate information security management
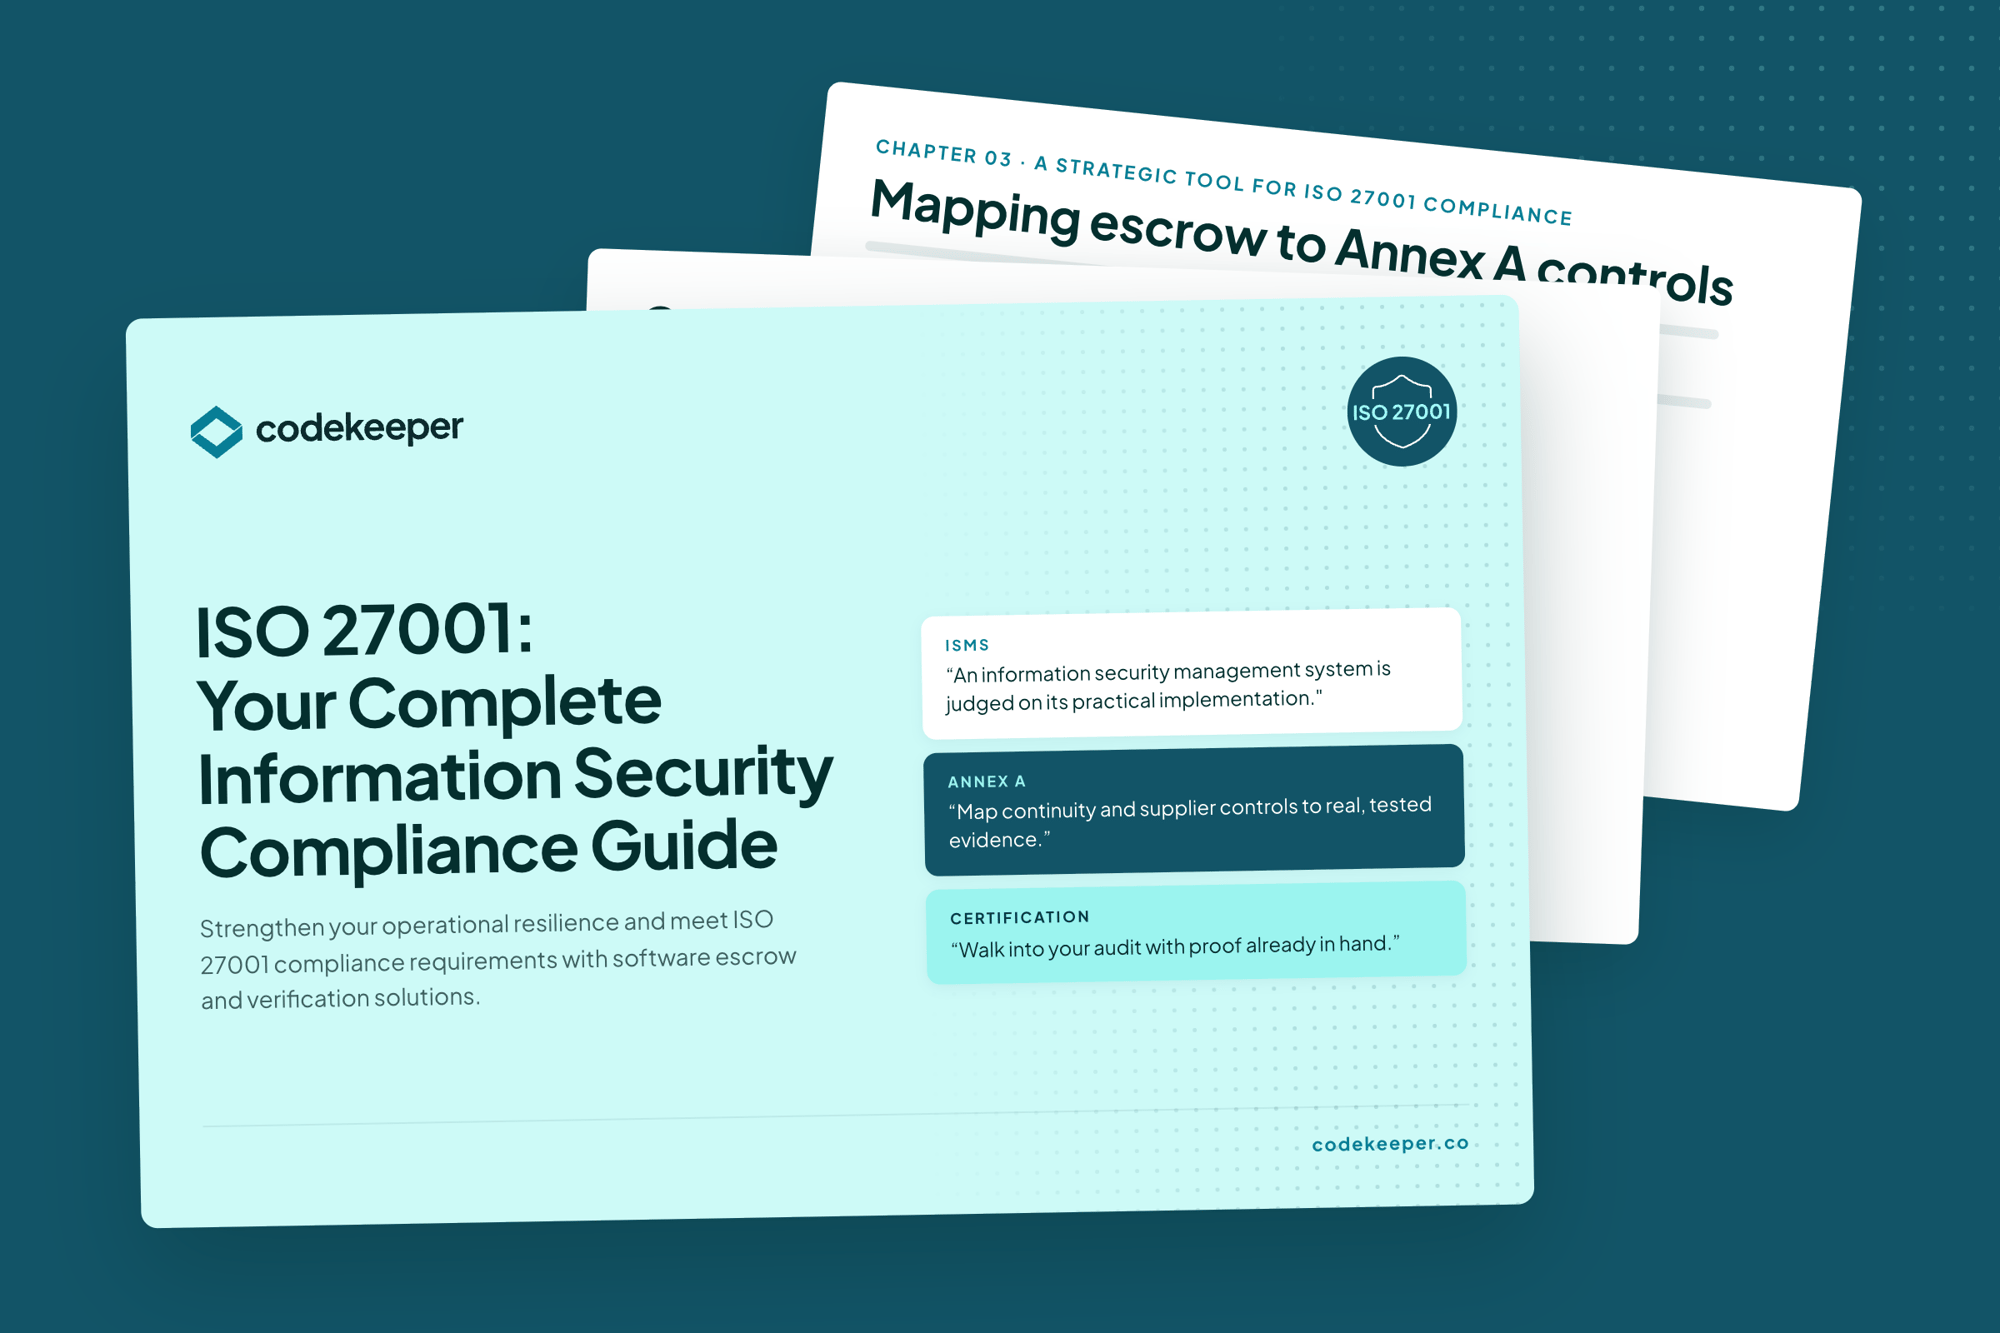
Prove recoverability to your auditors: Download the ISO 27001 guide
How you benefit from ISO 27001 readiness
Strengthen risk management and prevent incidents
Build stakeholder confidence and market credibility
Create systematic operational resilience
Shield your supplier relationships before gaps become crises
Good questions to ask first.
What is ISO 27001 in a nutshell?
ISO 27001 is the international standard for information security management. It provides a structured framework to protect your data through systematic risk assessments and security controls. While certification is voluntary, it's globally recognized as proof that your organization handles information security according to established best practices.
What are the three principles of ISO 27001?
ISO 27001 is built around the CIA triad: Confidentiality ensures only authorized people can access information, Integrity maintains data accuracy and completeness, and Availability guarantees information is accessible when needed. These three principles guide every security control and risk management decision within your ISMS.
Is ISO 27001 hard to get?
ISO 27001 certification is achievable with the right approach and commitment. The key is understanding why you need an ISMS and how your organization can align with the standard's requirements. Most organizations complete certification in six to 18 months, but building an effective ISMS requires ongoing commitment to continuous improvement and integrating security considerations into every business decision.
What is the difference between ISO 27001 and SOC 2?
ISO 27001 and SOC 2 serve different purposes in information security. ISO 27001 helps any organization establish a comprehensive information security management system, requiring you to build an entire risk-based framework with policies, procedures, and continuous improvement processes. SOC 2, on the other hand, is designed for service companies and evaluates their existing controls against predetermined criteria for security, availability, processing integrity, confidentiality, and privacy.
Why is software escrow important for ISO 27001 certification?
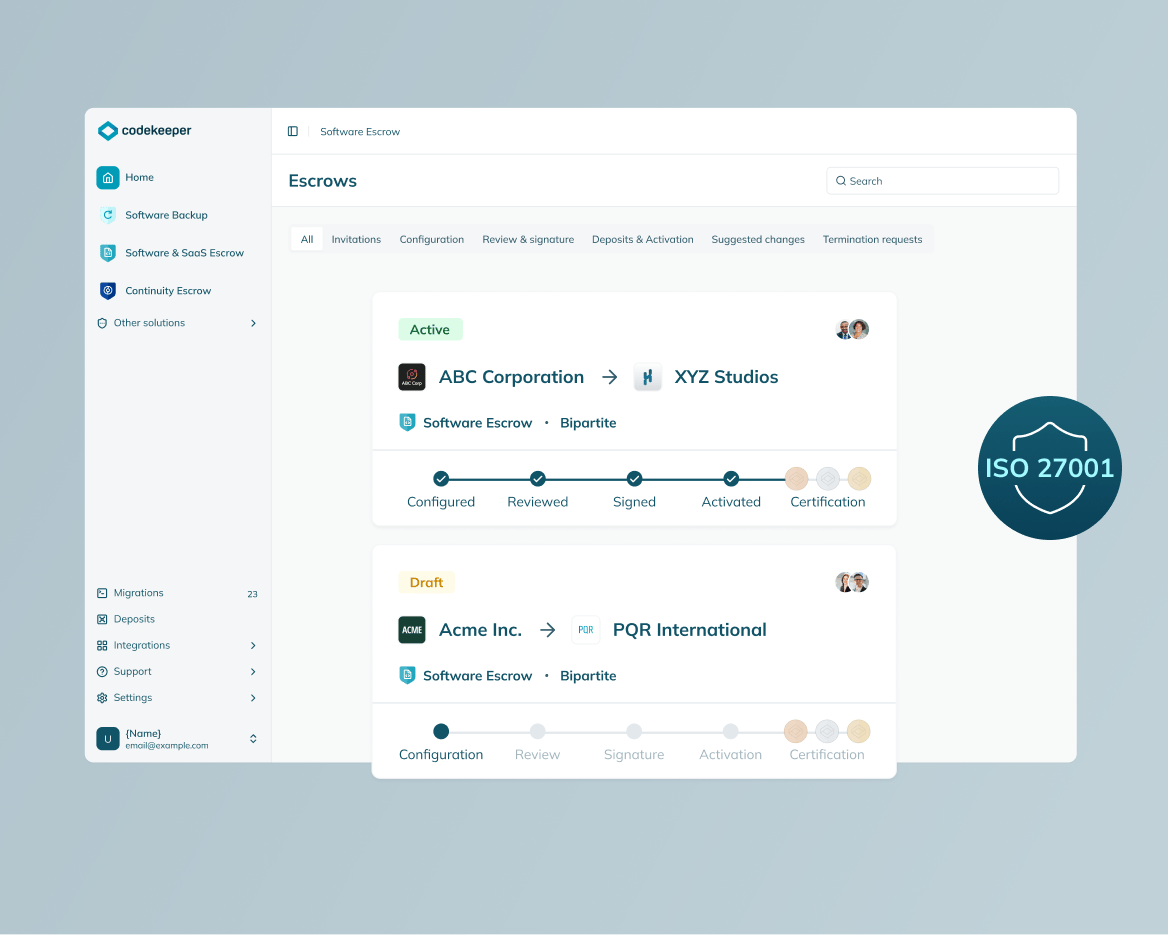
Software escrow aligns with ISO 27001 requirements for supplier relationship management and business continuity planning. When critical software vendors fail, escrow ensures continued access to source code and recovery materials. This provides auditable evidence of third-party risk mitigation that certification bodies expect to see during ISO 27001 assessments.
Can Codekeeper help with ISO 27001 readiness?
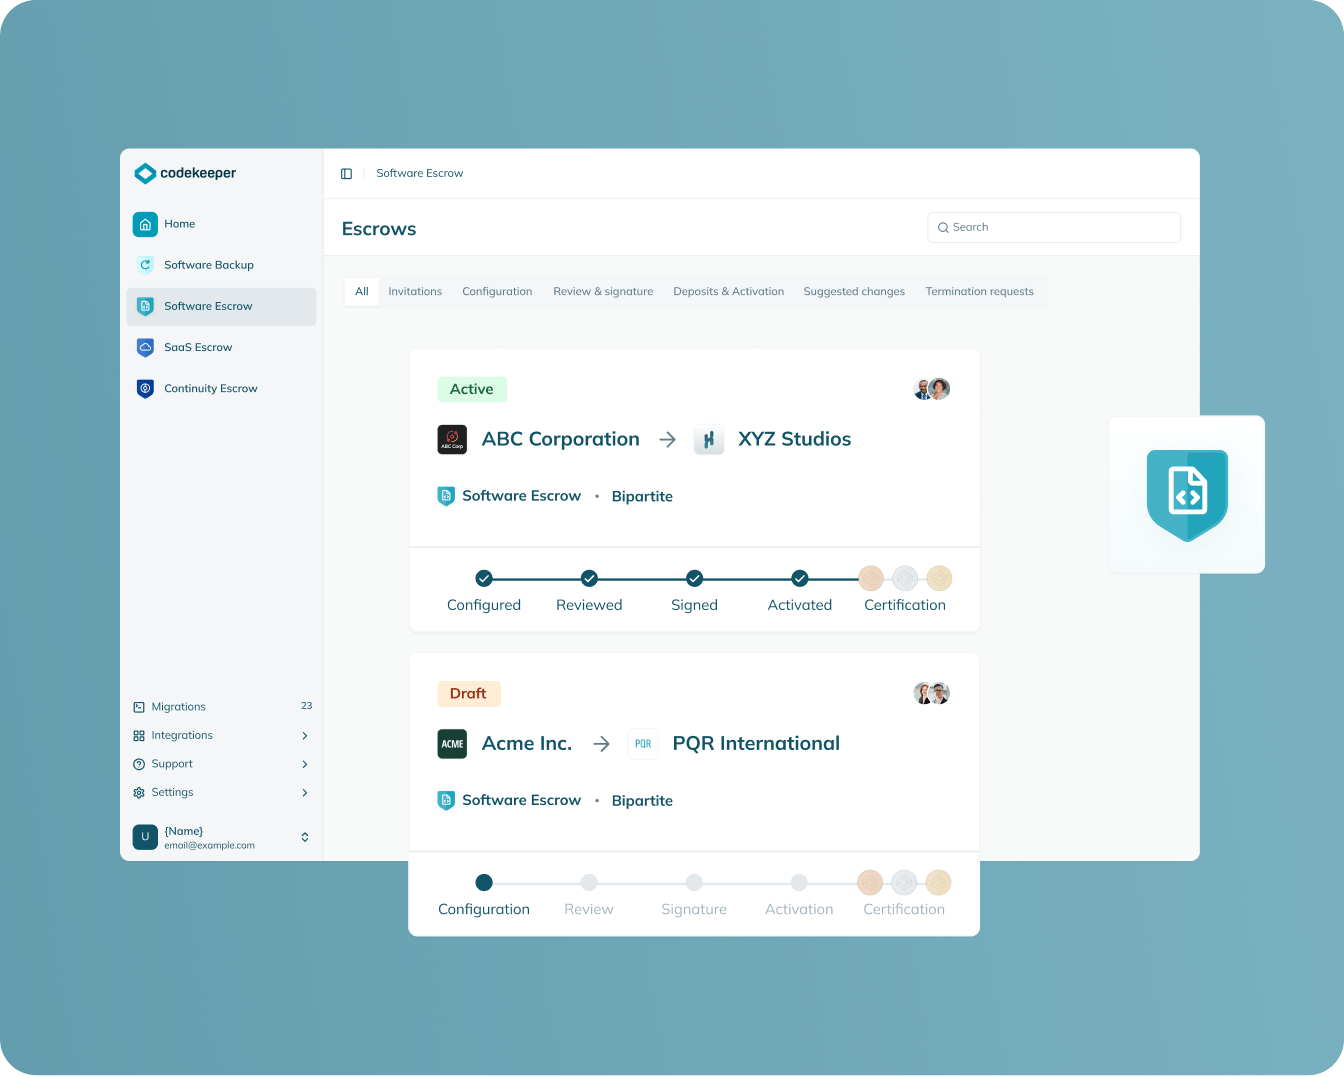
Yes, Codekeeper provides specialized software escrow solutions that address specific ISO 27001 control requirements around supplier relationships and operational resilience. Our platform secures critical software assets, establishes legal frameworks for vendor risk management, and generates compliance documentation, including Software Resilience Certificates.